01
Protected Identity & Access
Public-facing scans can reveal only information that is safe to show immediately while more sensitive data stays behind configured controls.
QAAR combines public-safe scan experiences with application-level encryption, protected access, organization policy and traceable operational history.
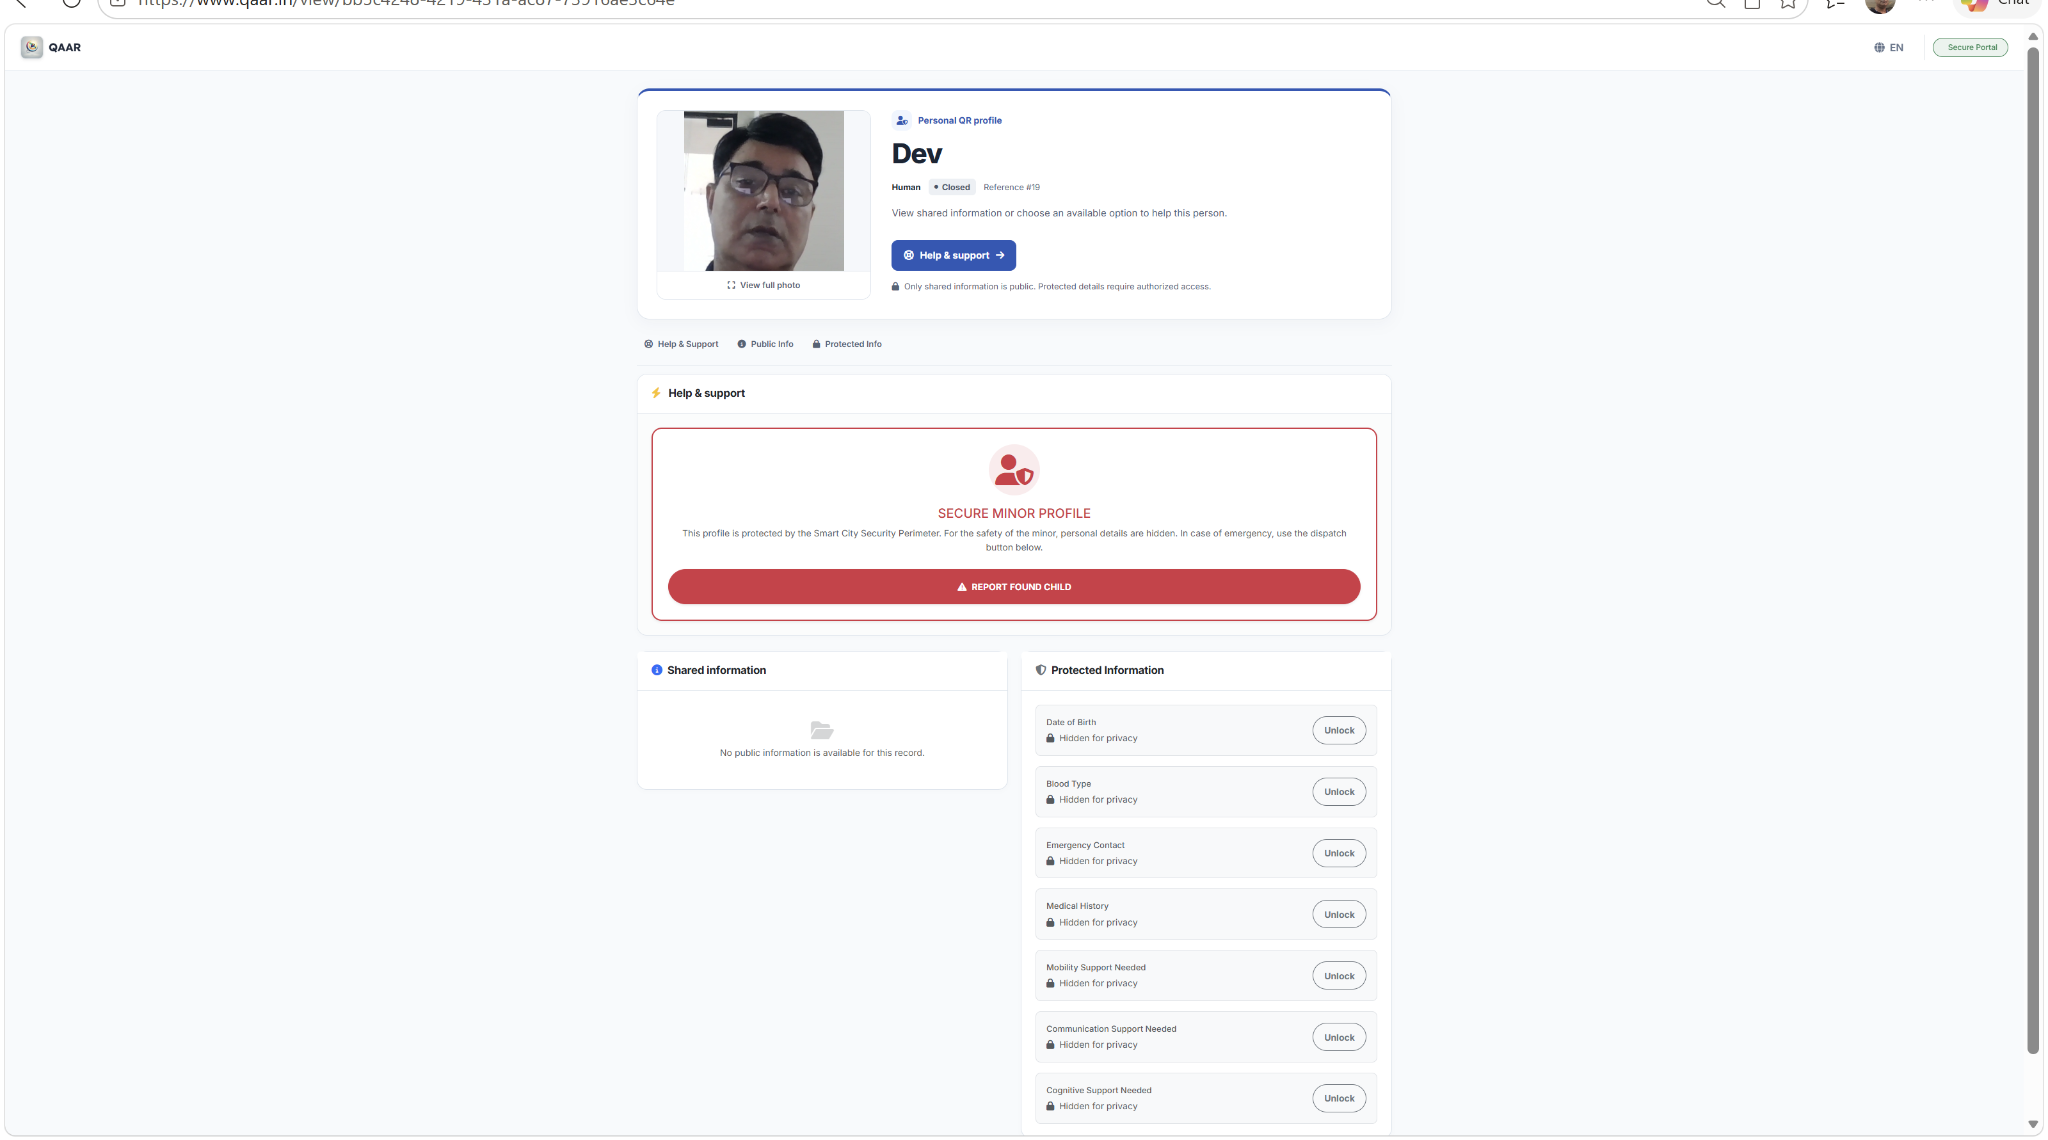
Public-facing scans can reveal only information that is safe to show immediately while more sensitive data stays behind configured controls.
Identity data, operational events, evidence and support actions remain distinct so they can follow appropriate policy.
Scans, relay actions, support responses, evidence and workflow state changes can be logged for review.
Scan instructions and support prompts can be presented across different language contexts.
The same platform can support individual and organization-managed workflows with role-aware access.
Configured dynamic record fields can be encrypted by the application before database storage. A global policy can force encryption on across those configured record fields.
Decide what a scanner can see immediately, what requires access control and what actions should be logged.